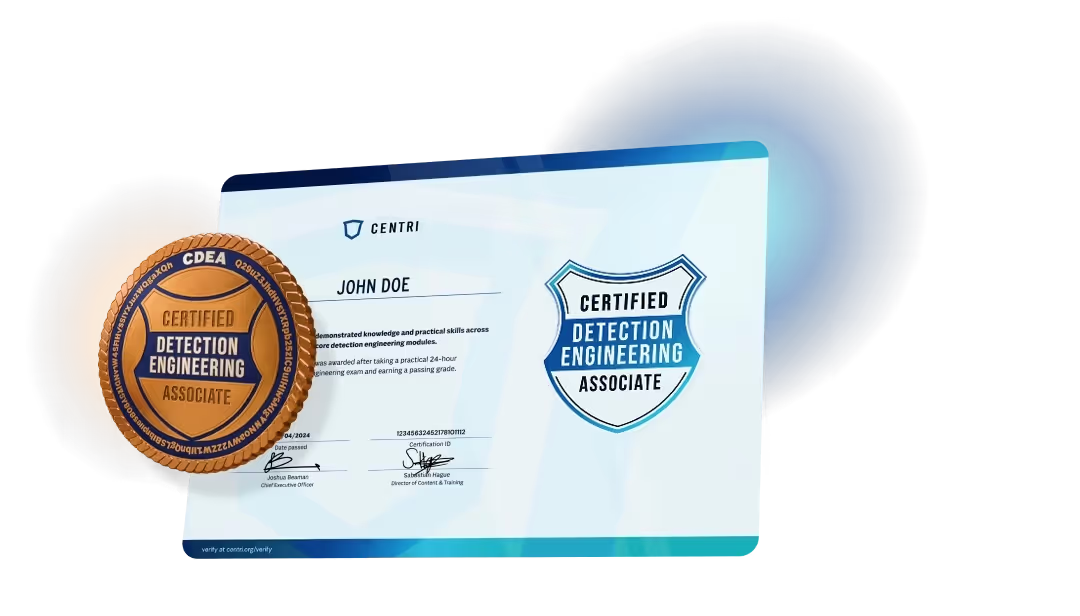
Certified Detection Engineering Associate (CDEA)
Lessons available in 9 languages with native text-to-speech (beta)
The CDEA (Certified Detection Engineering Associate) course develops practical detection engineering skills, focusing on how to design, build, test, and improve detections that help organizations identify and respond to threats. It is designed for cybersecurity professionals working in or around security operations, including SOC Analysts, Detection Engineers, SIEM Administrators, and Incident Response Analysts, who want to develop specialist detection engineering skills or strengthen their existing capabilities.
Skills you'll gain
Certified Detection Engineering Associate (CDEA)
Recommended experience
1-3 years experience
Estimated time to complete
approximately 40 hours to complete
On-demand access
Complete in 4 months
Training and exam price
£399.00 GBP
NICE Mapping
Infrastructure Support
57% Topics, 68% Knowledge, 81% Skills
Who is the course for?
CDEA is perfect for security professionals that want to develop their practical detection engineering skills. Roles that we believe would benefit from this course include:
- Security Analysts
- Incident Responders
- Threat Intelligence Analysts
- Security Engineers
- Detection Engineers
Whilst our content is aimed primarily at entry-level or junior roles, read our course syllabus to see if CDEA is the right choice for you or your team!
Why choose CDEA?
CDEA is designed to train students that are capable of responding to threat intelligence reports and are able to build test and deploy detections in your environments. Below are some examples of the skills and experience you will gain.
- Automate detection workflows with git.
- Creating and tuning network detection rules
- Creating and tuning Sigma Rules
- Utilising AI in detection engineering flows.
- … And much more
The skills and tools you’ll learn in this course will be directly applicable to a range of security roles, and are actively used by defenders around the world.
About the Course
2 topics
What You'll Learn
Lessons
- Welcome to the CDEA!
Networking Essentials
Windows Essentials
Linux Essentials
Python Essentials
Incident Response Essentials
Git Workflows for Detection Engineering
Network Analysis Essentials
Yara & Sigma Essentials
Zeek Essentials
Malware Analysis for Detection Engineering
Detection Rule Creation and Tuning
Threat Intelligence Integration for Detection
Behavioural Analytics for Threat Detection
AI for Defenders
CDEA Exam Preparation


Frequently asked questions
Will CDEA help me land my first detection job?
It gives you the skills hiring managers are looking for. CDEA is built to get you job-ready by focusing on the real tools, scenarios, and workflows used in modern detection environments.
Can I take CDEA if I already work in IT or another area of cybersecurity?
Yes. If you’re pivoting into detection roles or want to build detection-specific skills, CDEA helps bridge the gap and give you the confidence to step into a SOC role.
How is CDEA different from other junior cyber courses?
Many courses focus on broad cyber theory or compliance. CDEA is purpose-built for detection engineering. You’ll learn how to think and work like a detection engineer in a SOC environment, using the same tools and workflows.
What does the certification prove?
CDEA shows you can do the job. It’s a skills-first certification focused on detection engineering. You’ll leave with a portfolio of applied skills and a credential that helps you stand out in a crowded entry-level job market.
Is CDEA hands-on or just theory?
It’s practical from day one. You’ll learn detection engineering by doing, from working with real SOC tooling like Zeek, Splunk, and Elastic to managing CI/CD pipelines using Git.
How long does it take to complete CDEA?
The course is self-paced. Most learners will finish in 40-60 hours depending on their schedule and how deeply they engage with the labs and materials.
Do I need prior experience in detection engineering?
Whilst it would help, no. CDEA is made for professionals with 1-3 years’ cybersecurity experience. You’ll start with the basics and build up to real-world detection skills using industry-standard operational tools. If you’re a junior level analyst and possess curiosity about threat detection, you’re ready.